Passkeys and Phishing-Resistant MFA: What Makes Them Stronger Than SMS Codes?
Text-message codes are better than passwords alone, but stronger options exist. Here is why CISA recommends phishing-resistant authentication such as FIDO security keys and passkeys.
Last updated: October 8, 2026.
Two-factor authentication is now common, but not every second factor offers the same protection. Attackers can still trick people into typing one-time codes into fake login pages.
Why SMS Codes Are Better Than Passwords Alone
An attacker who steals only the password still needs another factor. That makes account takeover harder than password-only login.
Why SMS Still Has Weaknesses
Codes can be phished, intercepted in some scenarios, or exposed through account-recovery attacks. CISA ranks text and email codes below stronger MFA options.
What Makes FIDO Different
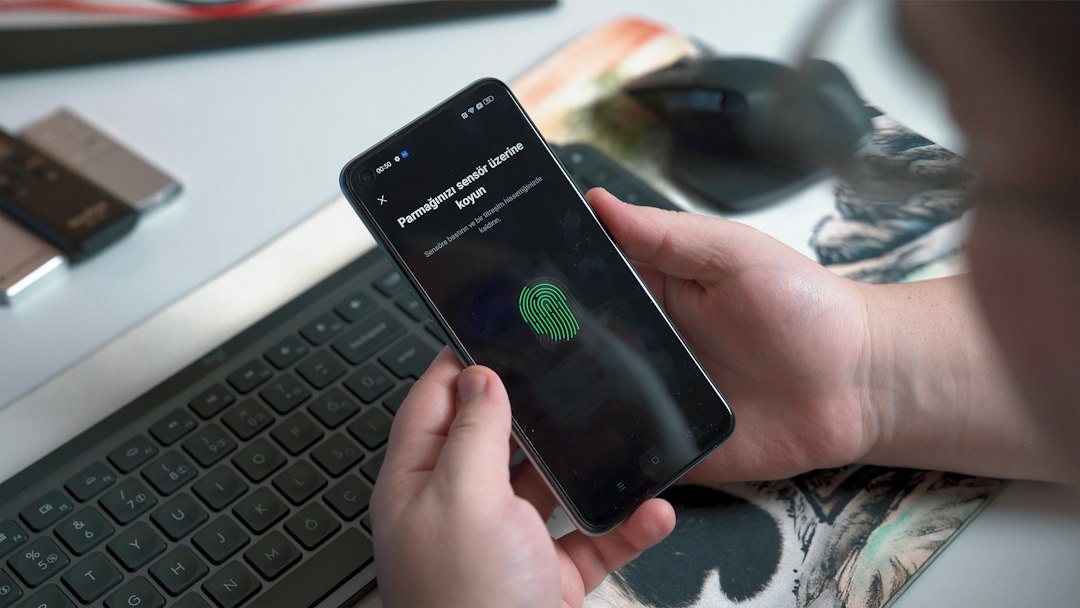
FIDO/WebAuthn authentication is bound to the legitimate website. That helps prevent a fake login page from replaying your credential against the real service.
Start With High-Value Accounts
Email, password managers, financial services and the accounts used to recover other accounts deserve the strongest authentication you can enable.
Related reading: U.S. Cyber Trust Mark buying guide · Deepfakes and online safety · Impersonation scams in 2026
The Bottom Line
Any MFA is generally better than no MFA, but when a service offers passkeys or security-key support, that is worth considering for accounts you cannot afford to lose.
Sources: CISA — More Than a Password; CISA — Mobile Communications Best Practice Guidance.
Get Free Daily Tips & Updates
Practical tips, money-saving ideas, useful guides, selected deals and helpful updates.